Open-source research initiative

Intelligence,
with boundaries.

Adaptive Intelligence for Secure & Resilient Distributed Systems

An open-source research initiative exploring explainable, risk-aware and adaptive authorization for secure and resilient cloud-native distributed systems.

Authorization / evolvingA → D
Implemented baselines and completed offline Model D researchSolid cyan layers represent implemented Models A, B and C. A double outer boundary represents completed experimental, non-enforcing offline Model D research.POLICYD / OFFLINECBA
The research direction

From explicit rules.
Toward bounded adaptation.

Model D · Research Implementation Complete
Observe. Assess. Authorize. Respond.

AI-Driven Automation for Resilient & Secure Cloud/Distributed Systems

01 / Research progression

A baseline for every next step.

Three implemented authorization baselines and a completed, experimental offline Model D research implementation.

Explore the Models

RBAC

Role-based access control establishes the deterministic authorization baseline.

Model A · ImplementedExplore Model A

RBAC + ABAC

Attribute-based conditions extend role-based authorization with request context.

Model B · ImplementedExplore Model B

Contextual Risk

Deterministic contextual risk adds explicit risk rules to role-based authorization.

Model C · ImplementedExplore Model C

Behavioral Adaptive Authorization

The bounded offline research implementation is complete; internal synthetic validation has been performed. Model D remains experimental and non-enforcing.

Model D · Research Implementation CompleteExplore Model D

Four research models: A → B → C → D. Swipe or scroll horizontally; keyboard users can focus the track and use arrow keys.

02 / System perspective

Understand the boundary. Then explore the system.

Investigating how identity, context, behavior and system state can inform authorization within explicit policy boundaries.

Explore the architecture
01 / Research architectureScope and status map
Implemented baseline · A–C · solid borderResearch implementation complete · D · double borderPlanned extension · dashed border

Implemented baseline · Models A–C

IdentityImplemented baseline · roles and attributes
ContextImplemented baseline · request evidence
Policy EngineImplemented baseline · deterministic policy
Contextual RiskImplemented baseline · deterministic rules
Baseline DecisionImplemented baseline · policy evaluation

Conceptual policy outcome vocabulary below belongs to the baseline path. Not every baseline implements every outcome. Model D cannot issue these actions.

ALLOWSTEP-UPLIMITDENY

Model D · Research implementation complete

Experimental offline scope only. Separate evidence and recommendation path; enforcement_authority=NONE. No access grants, denials or production control.

Behavioral inferenceResearch implementation complete · offline synthetic evidence
Eligibility and drift diagnosticsResearch implementation complete · bounded checks; robustness limitations remain
Experimental integrationResearch implementation complete · non-enforcing recommendations

Internal synthetic validation does not establish independent field effectiveness, mature drift monitoring or production readiness.

Planned extensions · no completed operational claim

Operational telemetryPlanned extension · live evidence pipeline
Adaptive decision integrationPlanned extension · production control, not Model D authority
Continuous feedbackPlanned extension · live closed-loop adaptation

Independent external validation remains unestablished. Offline mock feedback does not complete a live feedback loop.

Three statuses, not a product maturity scale: solid baseline, double-bordered completed experimental research, dashed planned extension. This conceptual scope map is not a deployment schematic or evidence of production enforcement. Models A–C implementation is recorded in the separate Research repository; this Portal does not independently establish effectiveness.
03 / The central question

What changes when authorization can adapt?

How does explainable, policy-bounded, closed-loop adaptive authorization perform relative to RBAC, ABAC and deterministic risk-aware authorization under behavioral and operational anomalies in cloud-native distributed systems?

Intelligent capabilities can be incorporated into system control loops while remaining bounded by deterministic engineering mechanisms, rather than simply added as an external service.

Toward reproducible experiments

04 / Build · Learn · Contribute

Build with the community.

Explore the community

AEGYTHON 2026

Turn curiosity into working software.

Explore the six challenges, qualification guidance and existing event program.

Explore AEGYTHON 2026
Confirmed schedule

Registration & Qualification: Oct 1 – Nov 6, 2026. Project Submission & Finalist Qualification: Nov 15 – Nov 22, 2026. Grand Finale: Nov 28, 2026.

Hackathon 2027

Coming Soon

A new chapter of innovation and collaboration. Details will be shared when officially confirmed.
Hackathon 2027 — Coming Soon

06 / Speaking & Presentations

View All Presentations
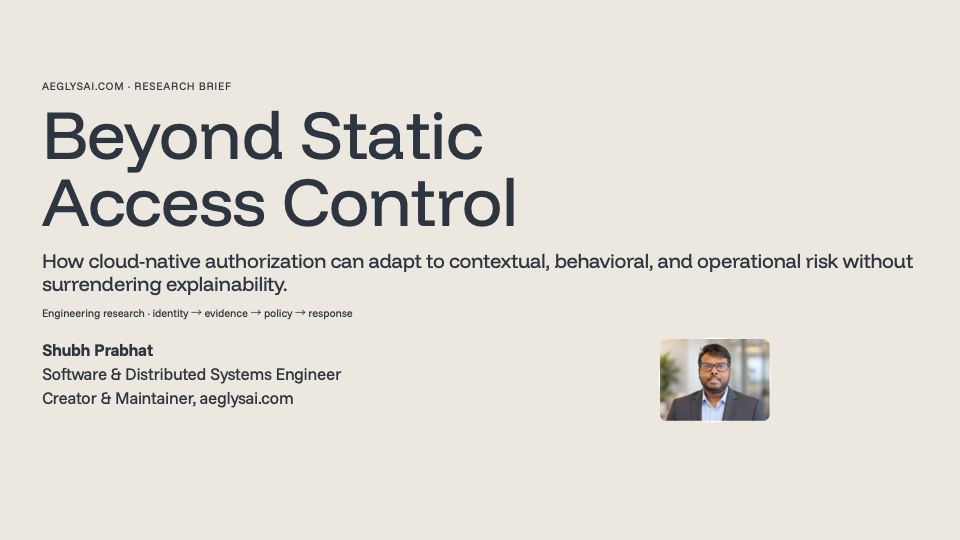
Approved first-slide preview · Full PDF not published.

Beyond Static Access Control: AI-Driven Adaptive Security for Resilient Cloud-Native Systems

A research brief on contextual, behavioral and operational risk in cloud-native authorization, explainable decisions and policy-bounded responses.

Completed · First-slide preview · Full PDF not publishedExplore presentation

Work in the open

Follow the research as it develops.

Research plans, architecture and work in preparation. Evidence will lead the conclusions.

About & Roadmap