Model A
RBAC
Role-based access control establishes the deterministic authorization baseline.
ImplementedObserve. Assess. Authorize. Respond.
An open-source research initiative exploring explainable, risk-aware and adaptive authorization for secure and resilient cloud-native distributed systems.
Intelligent capabilities can be incorporated into system control loops while remaining bounded by deterministic engineering mechanisms, rather than simply added as an external service.
From explicit rules.
Toward bounded adaptation.
AI-Driven Automation for Resilient & Secure Cloud/Distributed Systems
Three implemented authorization baselines and a completed, experimental offline Model D research implementation.
Role-based access control establishes the deterministic authorization baseline.
ImplementedAttribute-based conditions extend role-based authorization with request context.
ImplementedDeterministic contextual risk adds explicit risk rules to role-based authorization.
ImplementedThe bounded offline research implementation is complete; internal synthetic validation has been performed. Model D remains experimental and non-enforcing.
Research Implementation CompleteInvestigating how identity, context, behavior and system state can inform authorization within explicit policy boundaries.
Implemented baseline · Models A–C
Conceptual policy outcome vocabulary below belongs to the baseline path. Not every baseline implements every outcome. Model D cannot issue these actions.
Experimental offline scope only. Separate evidence and recommendation path; enforcement_authority=NONE. No access grants, denials or production control.
Internal synthetic validation does not establish independent field effectiveness, mature drift monitoring or production readiness.
Independent external validation remains unestablished. Offline mock feedback does not complete a live feedback loop.
How does explainable, policy-bounded, closed-loop adaptive authorization perform relative to RBAC, ABAC and deterministic risk-aware authorization under behavioral and operational anomalies in cloud-native distributed systems?
Toward reproducible experimentsExplore the six challenges, qualification guidance and existing event program.
Explore AEGYTHON 2026A new chapter of innovation and collaboration. Details will be shared when officially confirmed.
Hackathon 2027 — Coming Soon
Business Outstanders

Nerdbot
The Cyber Mag

Programming Insider

TechBullion
The Cyber Mag
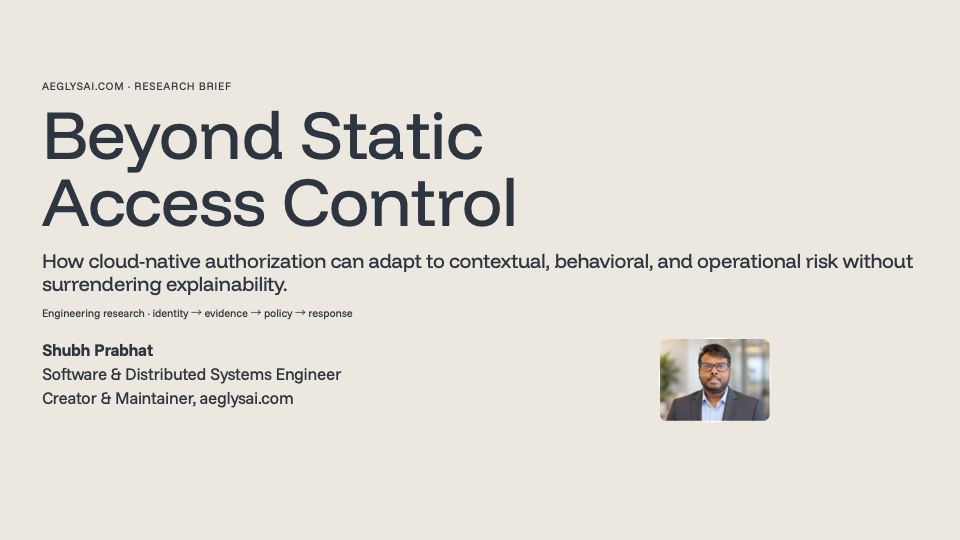
Adaptive Authorization / Zero Trust
A research brief on contextual, behavioral and operational risk in cloud-native authorization, explainable decisions and policy-bounded responses.
View Presentation : Beyond Static Access Control: AI-Driven Adaptive Security for Resilient Cloud-Native SystemsResearch plans, architecture and work in preparation. Evidence will lead the conclusions.